

Sanjay Kaushik
Managing Director, ASIS APAC Board Member
CFE, CII, FCIISCM, CATS, CCPS, CFAP

Managing Director, ASIS APAC Board Member
CFE, CII, FCIISCM, CATS, CCPS, CFAP
Director – Forensic Investigation
CII
Cyber incidents today extend far beyond system outages. Insider threats, data breaches, phishing campaigns, ransomware attacks, and business email compromise can disrupt operations, expose sensitive information, and create significant legal, regulatory, and financial consequences.
India recorded an all-time high average data breach cost of INR 220 million in 2025. Phishing, third-party and supply chain compromise, and vulnerability exploitation accounted for 48% of the initial attack vectors studied.
Source: IBM
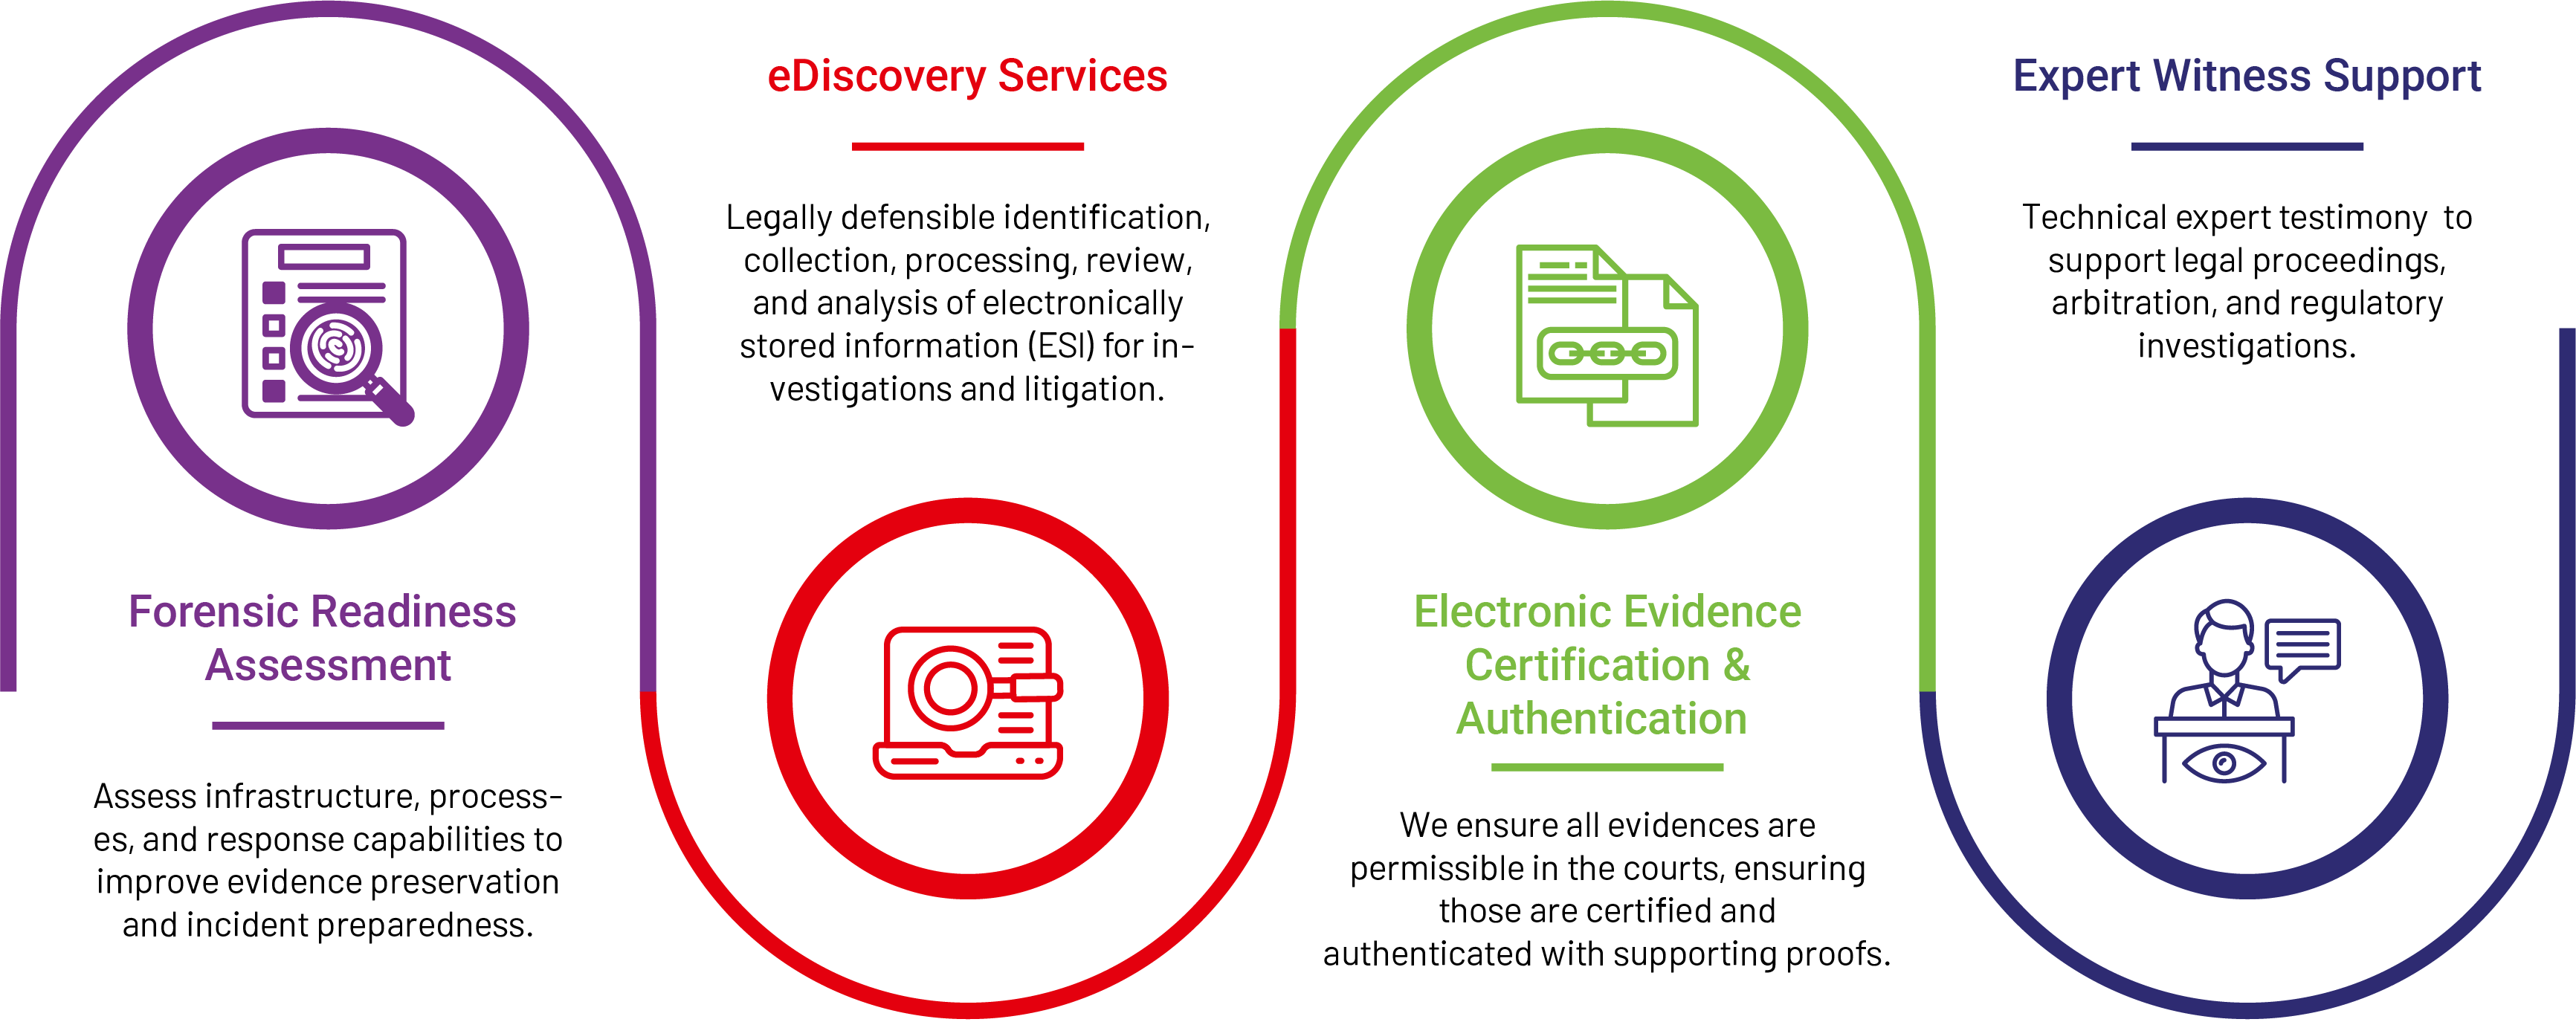
Netrika delivers end-to-end Digital Forensics & Incident Response (DFIR) services that help organisations investigate cyber incidents, preserve critical digital evidence, strengthen forensic readiness, and support legal and regulatory proceedings. Our multidisciplinary experts combine advanced forensic methodologies with industry-leading technologies to uncover facts, reconstruct incidents, and deliver legally defensible findings.
Recover, preserve, and analyse digital evidence across diverse environments while maintaining forensic integrity throughout the investigation lifecycle.
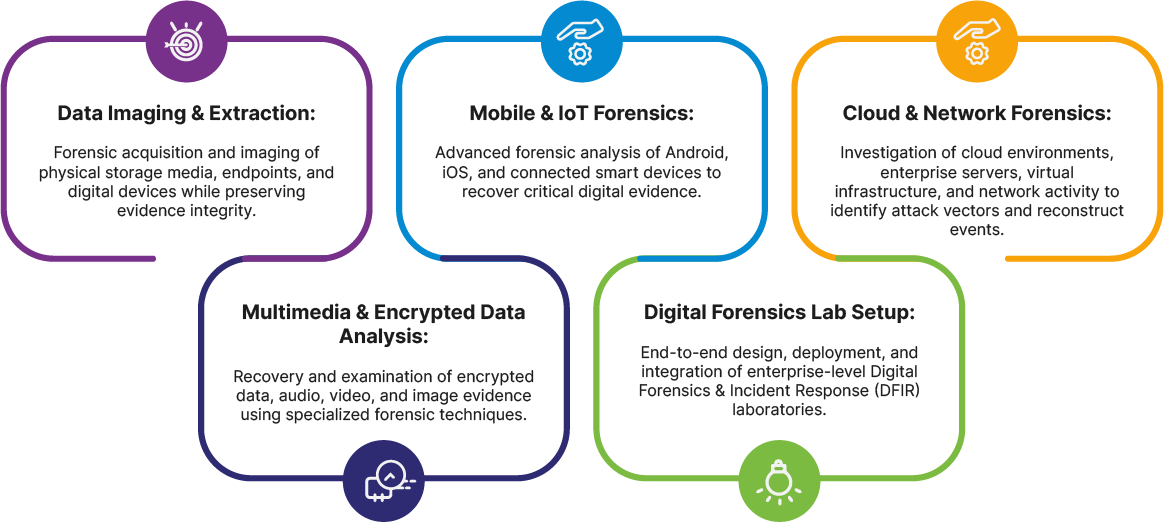
Rapidly identify, investigate, and contain cyber incidents while establishing the facts needed for informed business, legal, and regulatory decisions.
Strengthen organisational forensic readiness while ensuring investigations meet legal, regulatory, and evidentiary requirements.
Cyber incidents demand more than reactive investigations. Law Enforcements and organisations need dedicated forensic capabilities that enable rapid evidence acquisition, secure data handling, and legally defensible investigations. An enterprise-ready Digital Forensics & Incident Response (DFIR) lab provides the foundation to investigate incidents efficiently while maintaining the integrity of digital evidence throughout the forensic lifecycle.
What Do We Deliver?
A Digital Forensics & Incident Response (DFIR) lab is more than specialised hardware and software. It is a combination of secure infrastructure, standardised processes, and skilled resources working together to preserve evidentiary integrity and support efficient investigations.
An in-house DFIR capability enables organisations to respond faster, investigate with greater confidence, and reduce operational dependence during critical cyber incidents.
We help organisations to:
Accelerate incident response and investigation timelines
Preserve evidence integrity and legal defensibility

Maintain greater control over sensitive investigations

Reduce long-term dependency on external forensic responders

Strengthen organisational forensic readiness and resilience
Source: Seqrite
Avg. Response Time:
Rapid mobilization exceeding industry benchmarks, ensuring faster containment.
Threat Containment Success:
Efficient isolation and neutralization of threats, minimizing impact.
Evidence Integrity:
No legal disputes over data handling, maintaining full chain-of-custody compliance.
Client Satisfaction:
Remarkable client satisfaction from post-engagement feedback surveys.
Repeat Engagements:
Strong client trust drives repeat business for proactive DFIR solutions.
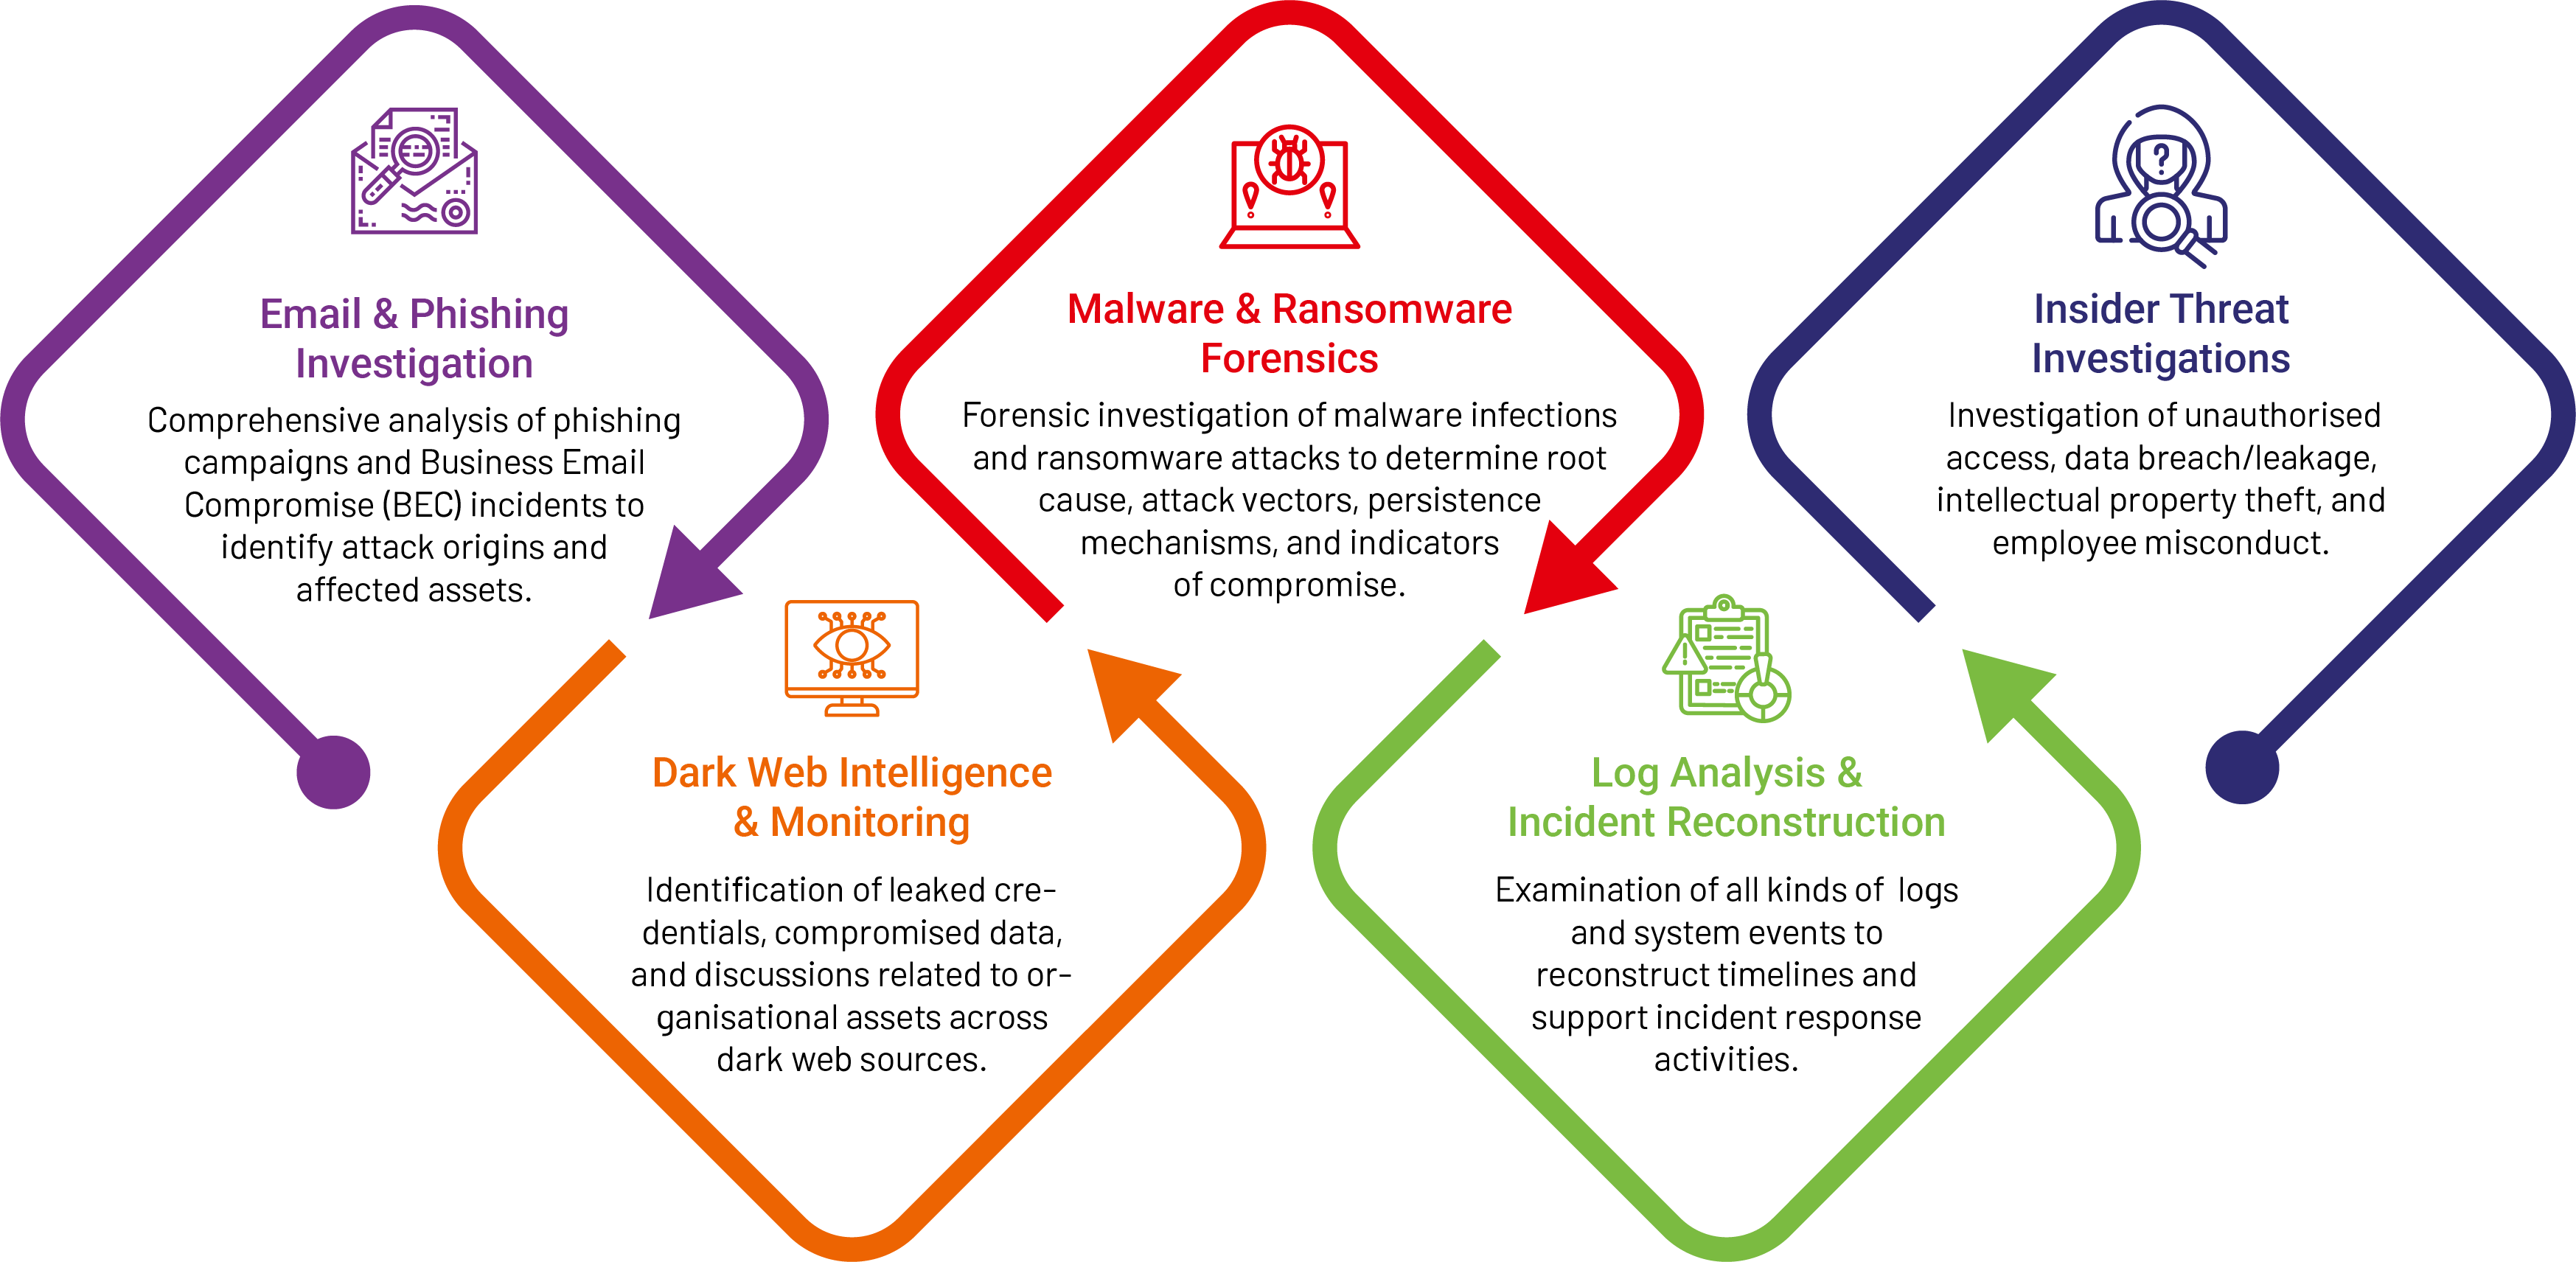
At Netrika, Digital Forensics and Incident Response is not viewed as a standalone technical exercise. We take a holistic approach that connects digital evidence, investigation, intelligence, security, risk, and business context to understand not only what happened, but why it happened, what it means for the organisation, and what needs to change.
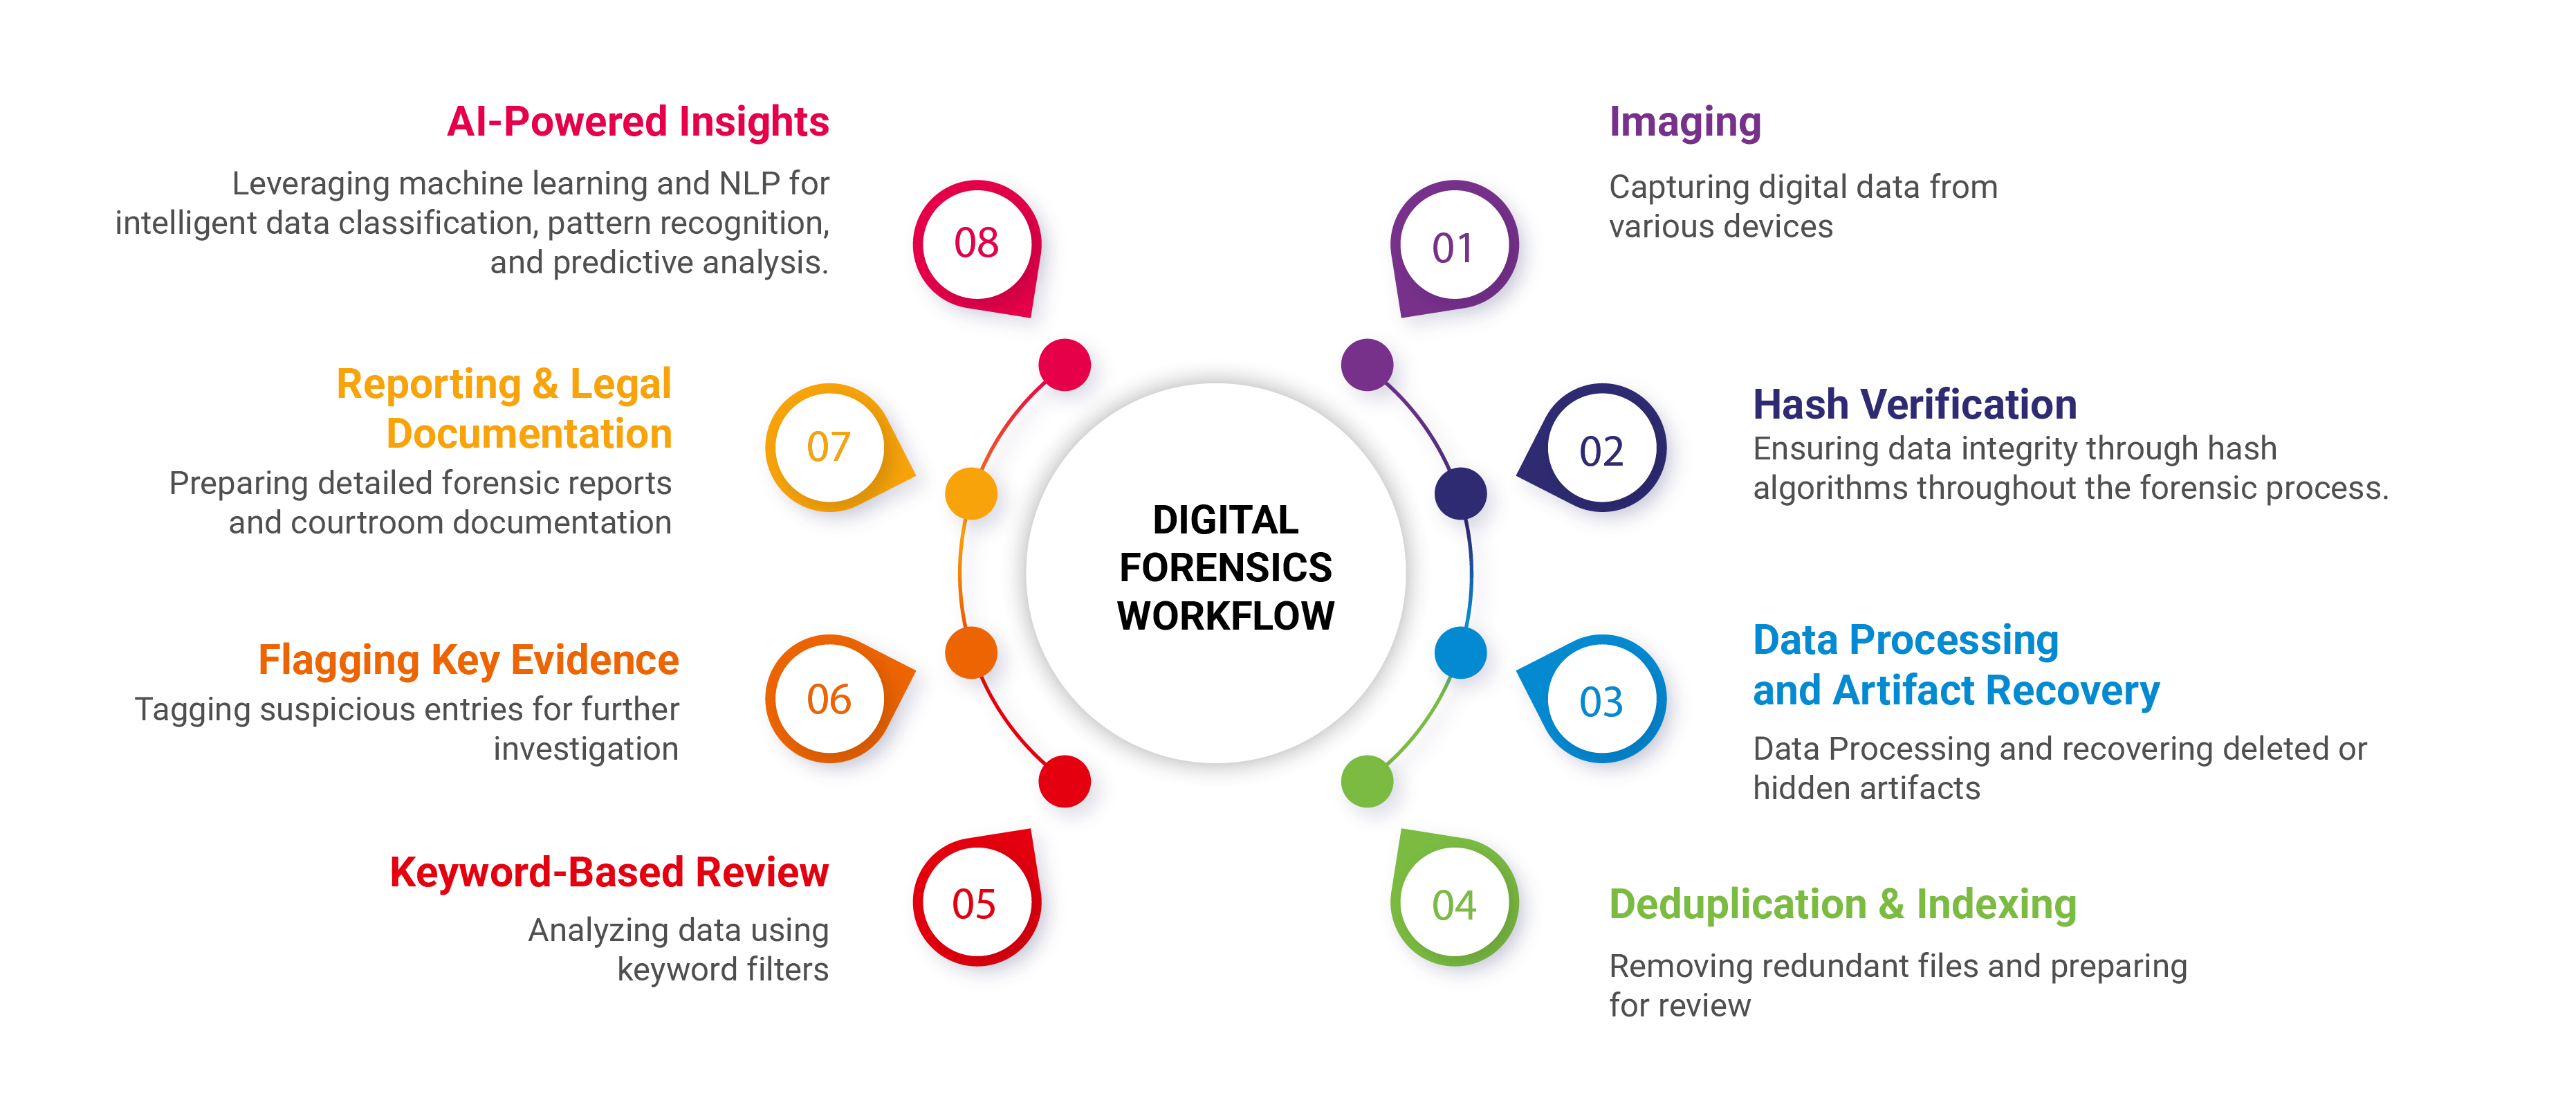
Our approach brings together forensic readiness, incident response, digital evidence acquisition, threat and behavioural analysis, cyber investigation, eDiscovery, intelligence and post-incident risk assessment. From endpoints, mobiles and networks to cloud environments, email and other digital sources, our specialists follow structured, forensically sound processes to identify, preserve and analyse evidence while maintaining defensibility and chain of custody. Netrika’s existing DFIR capability covers data extraction and analysis, disk imaging, mobile and cloud forensics, email investigation, social media discovery, network forensics and video and image forensics.
The outcome is more than an investigation. It is actionable intelligence that helps organisations detect, respond, recover and strengthen their overall risk posture.
Source: Seqrite
A digital incident rarely remains a digital problem. A breach can become a fraud investigation, a regulatory matter, a litigation challenge, a reputational issue or a wider business risk. Netrika brings these interconnected capabilities together under one enterprise risk management ecosystem, enabling organisations to address the incident and the risks surrounding it through a single, multidisciplinary partner.
Our AI-powered Forensics capability combines technology-assisted analysis with experienced forensic expertise to accelerate the identification and review of relevant evidence across large and complex datasets. This is supported by end-to-end Digital Forensics and Incident Response, covering investigation, evidence preservation, analysis, incident response and post-incident recommendations. Our broader capabilities across forensic investigation, security and risk consulting, due diligence, information security, brand protection, background checks and intelligence allow us to connect individual incidents to wider organisational risk.
With an established presence across major regions and capabilities supporting pan-India coverage, Netrika brings local understanding, multidisciplinary expertise and technology-enabled investigation to organisations wherever the risk emerges.
Whether you're responding to a cyber incident, investigating digital fraud, or strengthening forensic readiness, Netrika helps organisations respond with speed, preserve digital evidence, and investigate with confidence.
CFE, CII, FCIISCM, CATS, CCPS, CFAP
CII
Speak with our team at the nearest Netrika office or connect with us online.

Digital forensics and incident response are branches of cybersecurity that involve identifying, investigating, containing, remediating and potentially testifying related to cyberattacks, litigations or other digital investigations.
Digital forensics and incident response (DFIR) is a specialized field focused on identifying, remediating, and investigating cybersecurity incidents. As the name suggests, DFIR consists of two related components: Digital forensics involves collecting, preserving, and analyzing forensic evidence. Incident Response is a systematic process designed to address and resolve cybersecurity threats or data breaches. It focuses on identifying, assessing, containing, and eliminating incidents while ensuring minimal disruption to operations. This approach also safeguards critical evidence for subsequent analysis and supports swift recovery to normalcy.
Computer forensics is a field of technology that uses investigative techniques to identify and store evidence from a computer device. Often, computer forensics is used to uncover evidence that could be used in a court of law.
DF is a standard based methodology that can allow post-breach monitoring with alerts. It also enables swift reaction in the event of an incident, and the forensically preserved data proves crucial to the investigation and reporting phases.
Digital forensic investigators are professionals who specialize in collecting, analyzing, and preserving electronic evidence to be used in legal proceedings. These investigators are trained in techniques to recover data from computers, mobile devices, and other digital storage media.